Comment gérer les cas SOC
En savoir plus


The rest of this article breaks down what’s actually required, why CISA made the change now, and how security teams, federal or not, can operationalize it without adding headcount.
BOD 26-04 is a Binding Operational Directive from the Cybersecurity and Infrastructure Security Agency (CISA) that changes how federal agencies decide lequel vulnerabilities to patch first and how fast. Instead of treating every vulnerability in the KEV catalog the same way, or leaning on a static CVSS score, agencies must now score each vulnerability against four real-world risk signals and remediate on a graduated timeline tied to that score.
CISA frames this as a shift from compliance-driven patching à risk-driven patching: the goal isn’t to close every CVE on a list, it’s to close the ones that are actually reachable, actively exploited, easy to automate, and capable of doing real damage, first.
BOD 26-04 formally replaces two earlier directives:
Two trends collided. First, remediation performance was getting worse, not better: per the 2026 Verizon Data Breach Investigations Report, only 26% of KEV-listed vulnerabilities were fully remediated in 2025, down from 38% the year before, and median remediation time climbed to 43 days, even as exploitation of known vulnerabilities remained a leading initial access vector. Flat deadlines weren’t producing faster patching; they were producing patch fatigue.
Second, CISA has been explicit that AI is compressing the window between vulnerability disclosure and weaponization. When adversaries can use AI to go from a published CVE to a working exploit in days, a one-size-fits-all 14-day clock is both too slow for the vulnerabilities that matter most and too demanding for the ones that don’t. BOD 26-04 is CISA’s answer: move the fastest agencies have ever been asked to move (3 days) for the small slice of vulnerabilities that are genuinely dangerous, and give real relief, deferral to the next system upgrade, for the majority that aren’t.
Every vulnerability, on every asset, gets evaluated against four questions:
This is a decision tree, not a checklist; the combination of factors determines the remediation tier, not simply how many boxes are checked. Take a system off the public internet, and its clock changes even though the underlying vulnerability is still unpatched. That single design choice is why BOD 26-04 leans so heavily on continuous, accurate asset inventory rather than point-in-time scans.
BOD 26-04 replaces BOD 22-01’s two timelines with a graduated, five-tier model:
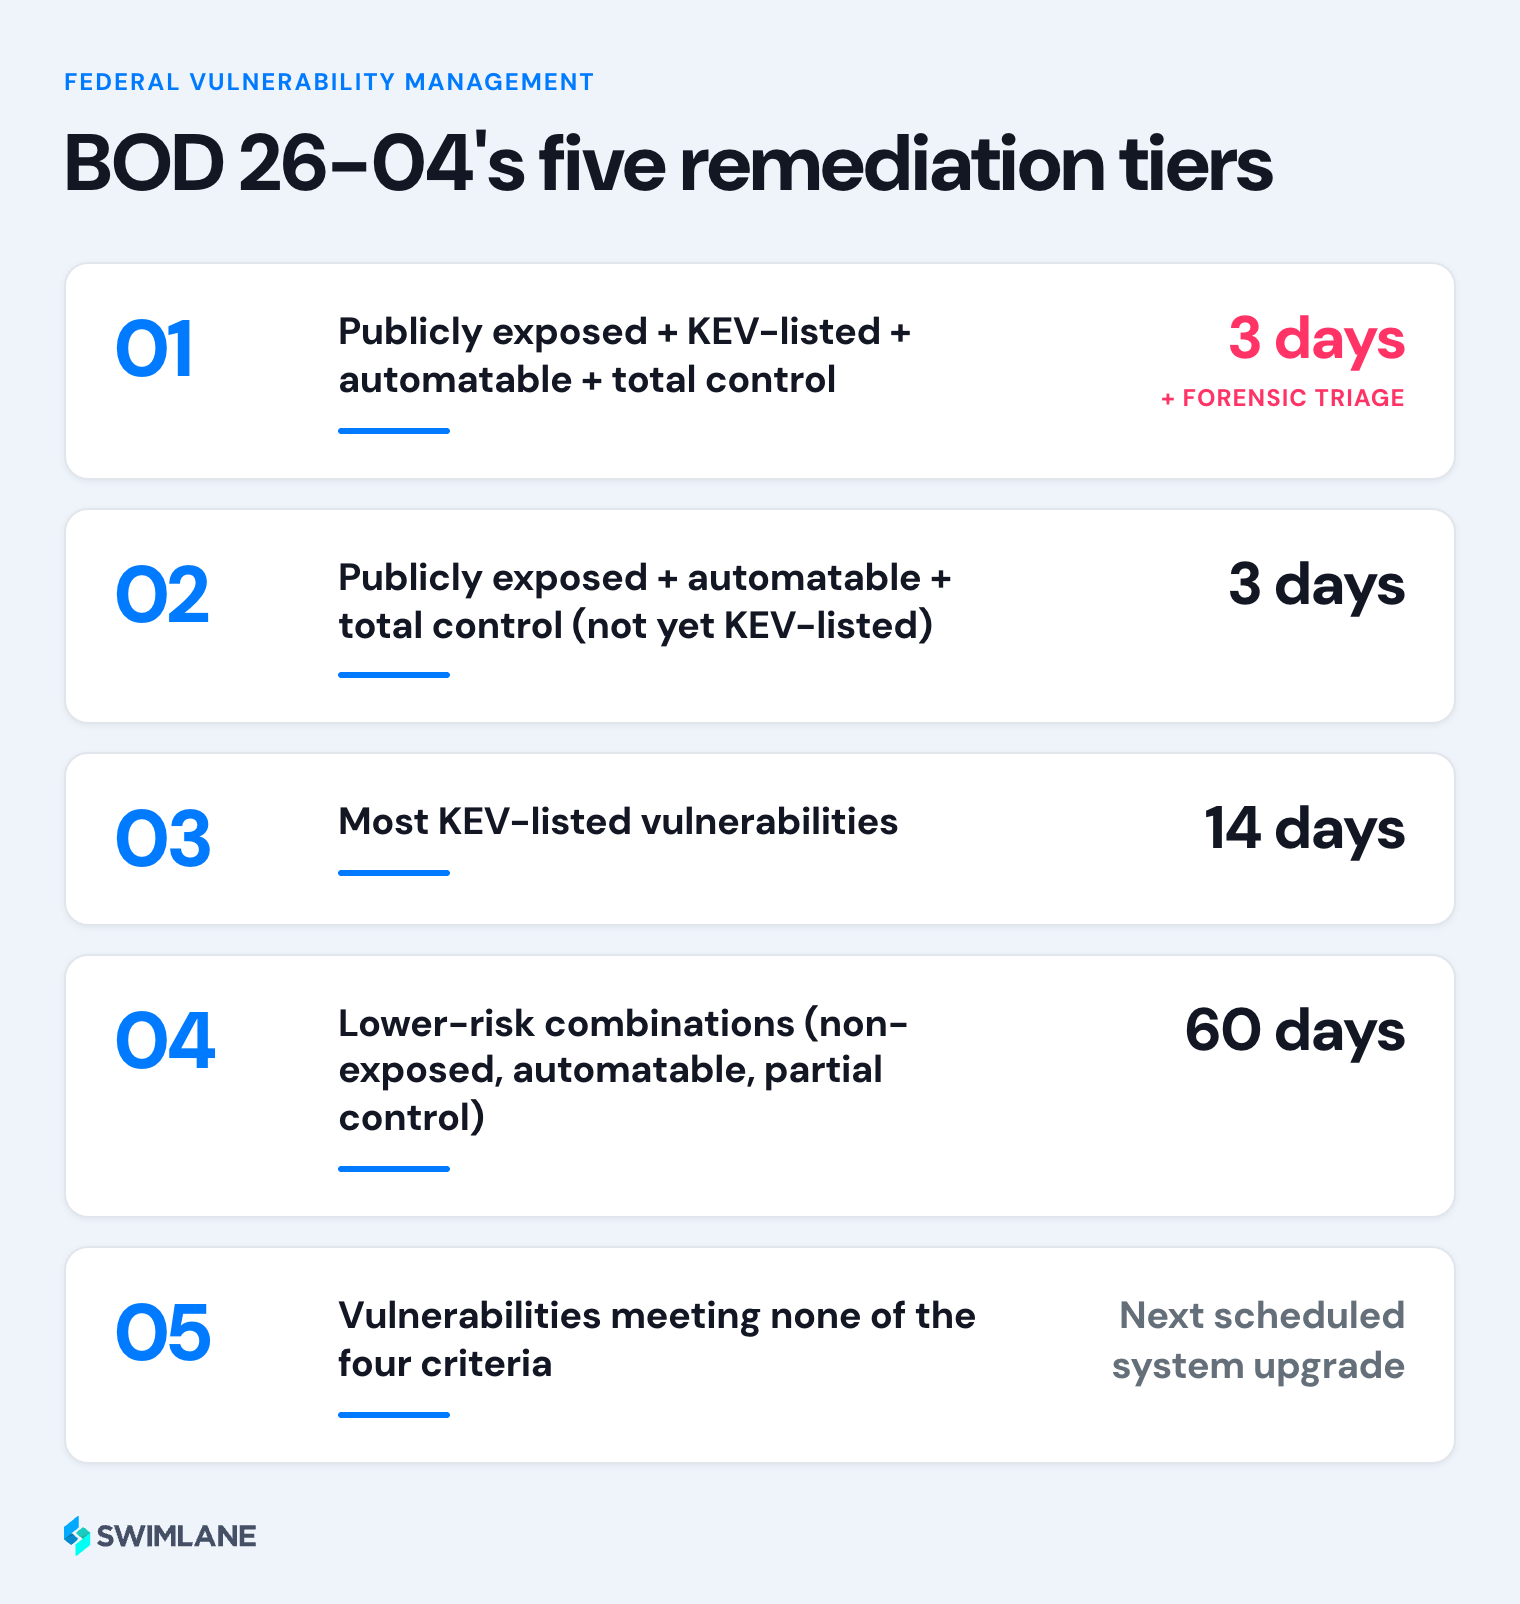
| Profil de risque | Remediation Window |
|---|---|
| Publicly exposed + KEV-listed + automatable + total control | 3 days, plus mandatory forensic triage for prior compromise |
| Publicly exposed + automatable + total control (not yet KEV-listed) | 3 days |
| Most KEV-listed vulnerabilities | 14 days |
| Lower-risk combinations (non-exposed, automatable, partial control) | 60 days |
| Vulnerabilities meeting none of the four criteria | Fix on next scheduled system upgrade |
Early analysis at one large civilian agency found that only about 1% of vulnerability instances fell into the 3-day tier, while more than 60% qualified for deferral to the next system upgrade, evidence that the model is designed to concentrate urgency, not spread it evenly.
| Date | Requirement |
|---|---|
| December 7, 2026 | Agencies must meet the full remediation timelines defined in the directive |
| December 7, 2026 | FedRAMP-authorized cloud service providers must implement Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER) rulesets |
| March 7, 2027 | Deadline for FedRAMP corrective action plans; non-compliant cloud services risk losing FedRAMP authorization after this date |
BOD 26-04 is binding for Federal Civilian Executive Branch (FCEB) agencies. It does not directly bind federal contractors or private companies, but the practical reach is broader:
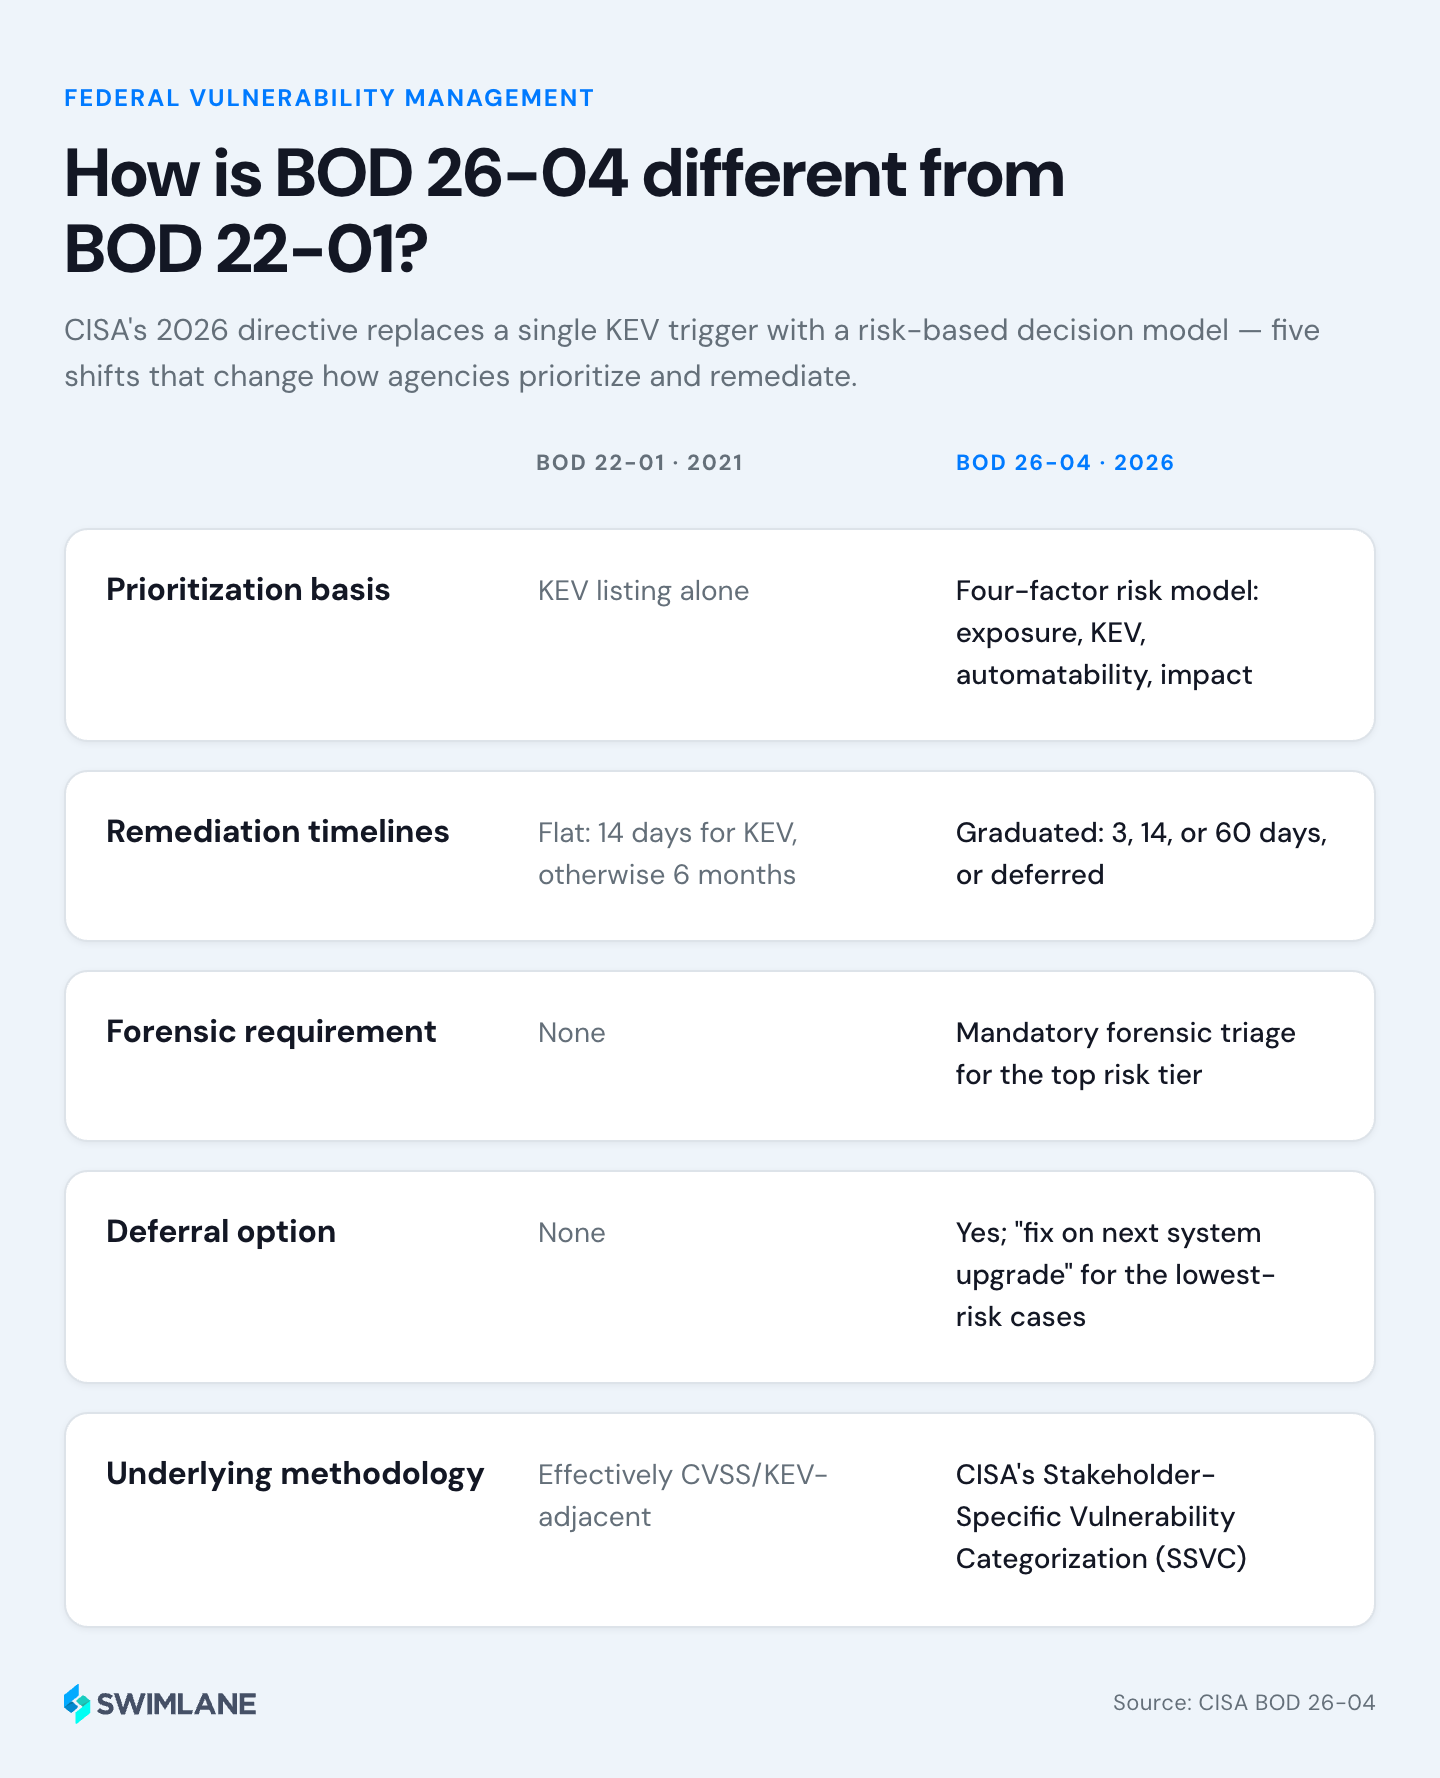
| BOD 22-01 (2021) | BOD 26-04 (2026) | |
|---|---|---|
| Prioritization basis | KEV listing alone | Four-factor risk model (exposure, KEV, automatability, impact) |
| Timelines | Flat: 14 days (KEV) or 6 months | Graduated: 3/14/60 days, or deferred |
| Forensic requirement | Aucun | Mandatory triage for the top risk tier |
| Deferral option | Aucun | Yes; “fix on next system upgrade” for lowest-risk cases |
| Underlying methodology | Effectively CVSS/KEV-adjacent | CISA’s Stakeholder-Specific Vulnerability Categorization (SSVC) |
Meeting a 3-day clock, especially one that includes forensic triage, is not a policy update… It’s an infrastructure and workflow problem. In practice, BOD 26-04 requires:
For most organizations, the honest gap isn’t a policy gap; it’s that no team can manually re-run this four-variable decision across a growing asset inventory every time CISA updates KEV or Vulnrichment data.
Before getting into tooling, run your current program through these six questions; they’re the ones an auditor, an Inspector General, or a determined attacker will effectively be asking:
If more than one or two of those are “no,” the gap isn’t policy; it’s automation and visibility. That’s exactly the gap Swimlane customers are positioned to close quickly, and where most prospective customers start the conversation.
| BOD 26-04 Requirement | What It Demands | How Swimlane Vulnerability Response Management Delivers It |
|---|---|---|
| Continuous asset exposure assessment | A real-time answer to “is this reachable from the internet,” not a stale CMDB tag | Intégrations autonomes pull live data from asset inventories, CMDBs, and exposure tools into one centralized, correlated view |
| KEV / Vulnrichment ingestion | Automatic pickup of CISA’s KEV catalog and exploitability data the moment it’s published | Swimlane Intelligence (part of VRM) enriches findings, including known exploits, VCSS scores, EPSS scores and 30+ customizable enrichment sources |
| Four-factor risk scoring | Combine exposure, KEV status, automatability, and impact per asset, continuously | The VRM Prioritization Rank uses Swimlane Intelligence to automatically assess risk and prioritize responses, factoring in exceptions to reduce unnecessary alerts. |
| 3-day tier response | Immediate triage and action with no manual bottleneck | Turbine’s vulnerability finding automated grouping correlates CVEs to assets and business owners, shrinking the time to find and triage to minutes |
| Mandatory forensic triage | Evidence collection and compromise assessment before or alongside patching | Streamline vulnerability tracking and remediation recommendations with VRM’s case management application, which integrates with leading ITSM and collaboration tools. |
| SLA enforcement across all tiers | Programmatic, auditable timeline tracking for 3/14/60-day and deferred vulnerabilities | SLA tracking and dynamic asset risk are evaluated and combined. Turbine Canvas playbooks encode all five tiers, so enforcement doesn’t depend on someone remembering a deadline. |
| Defensible audit trail | Documentation an Inspector General or auditor can actually review | Every automated decision and escalation is logged and explainable, not a black box. In-depth inference available via Hero AI. |
Organizations running Solution de gestion des réponses aux vulnérabilités (VRM) Swimlane have reported 30% faster vulnerability patching and 92% Auto-remediation.
Your Swimlane account team can help scope this in a working session.
If you’re evaluating Swimlane: BOD 26-04 is a useful stress test for whatever you’re running today, can it actually hit a 3-day clock with an audit trail attached, at your scale? See the AI SOC datasheet for the technical detail, or request a walkthrough built around your own environment.
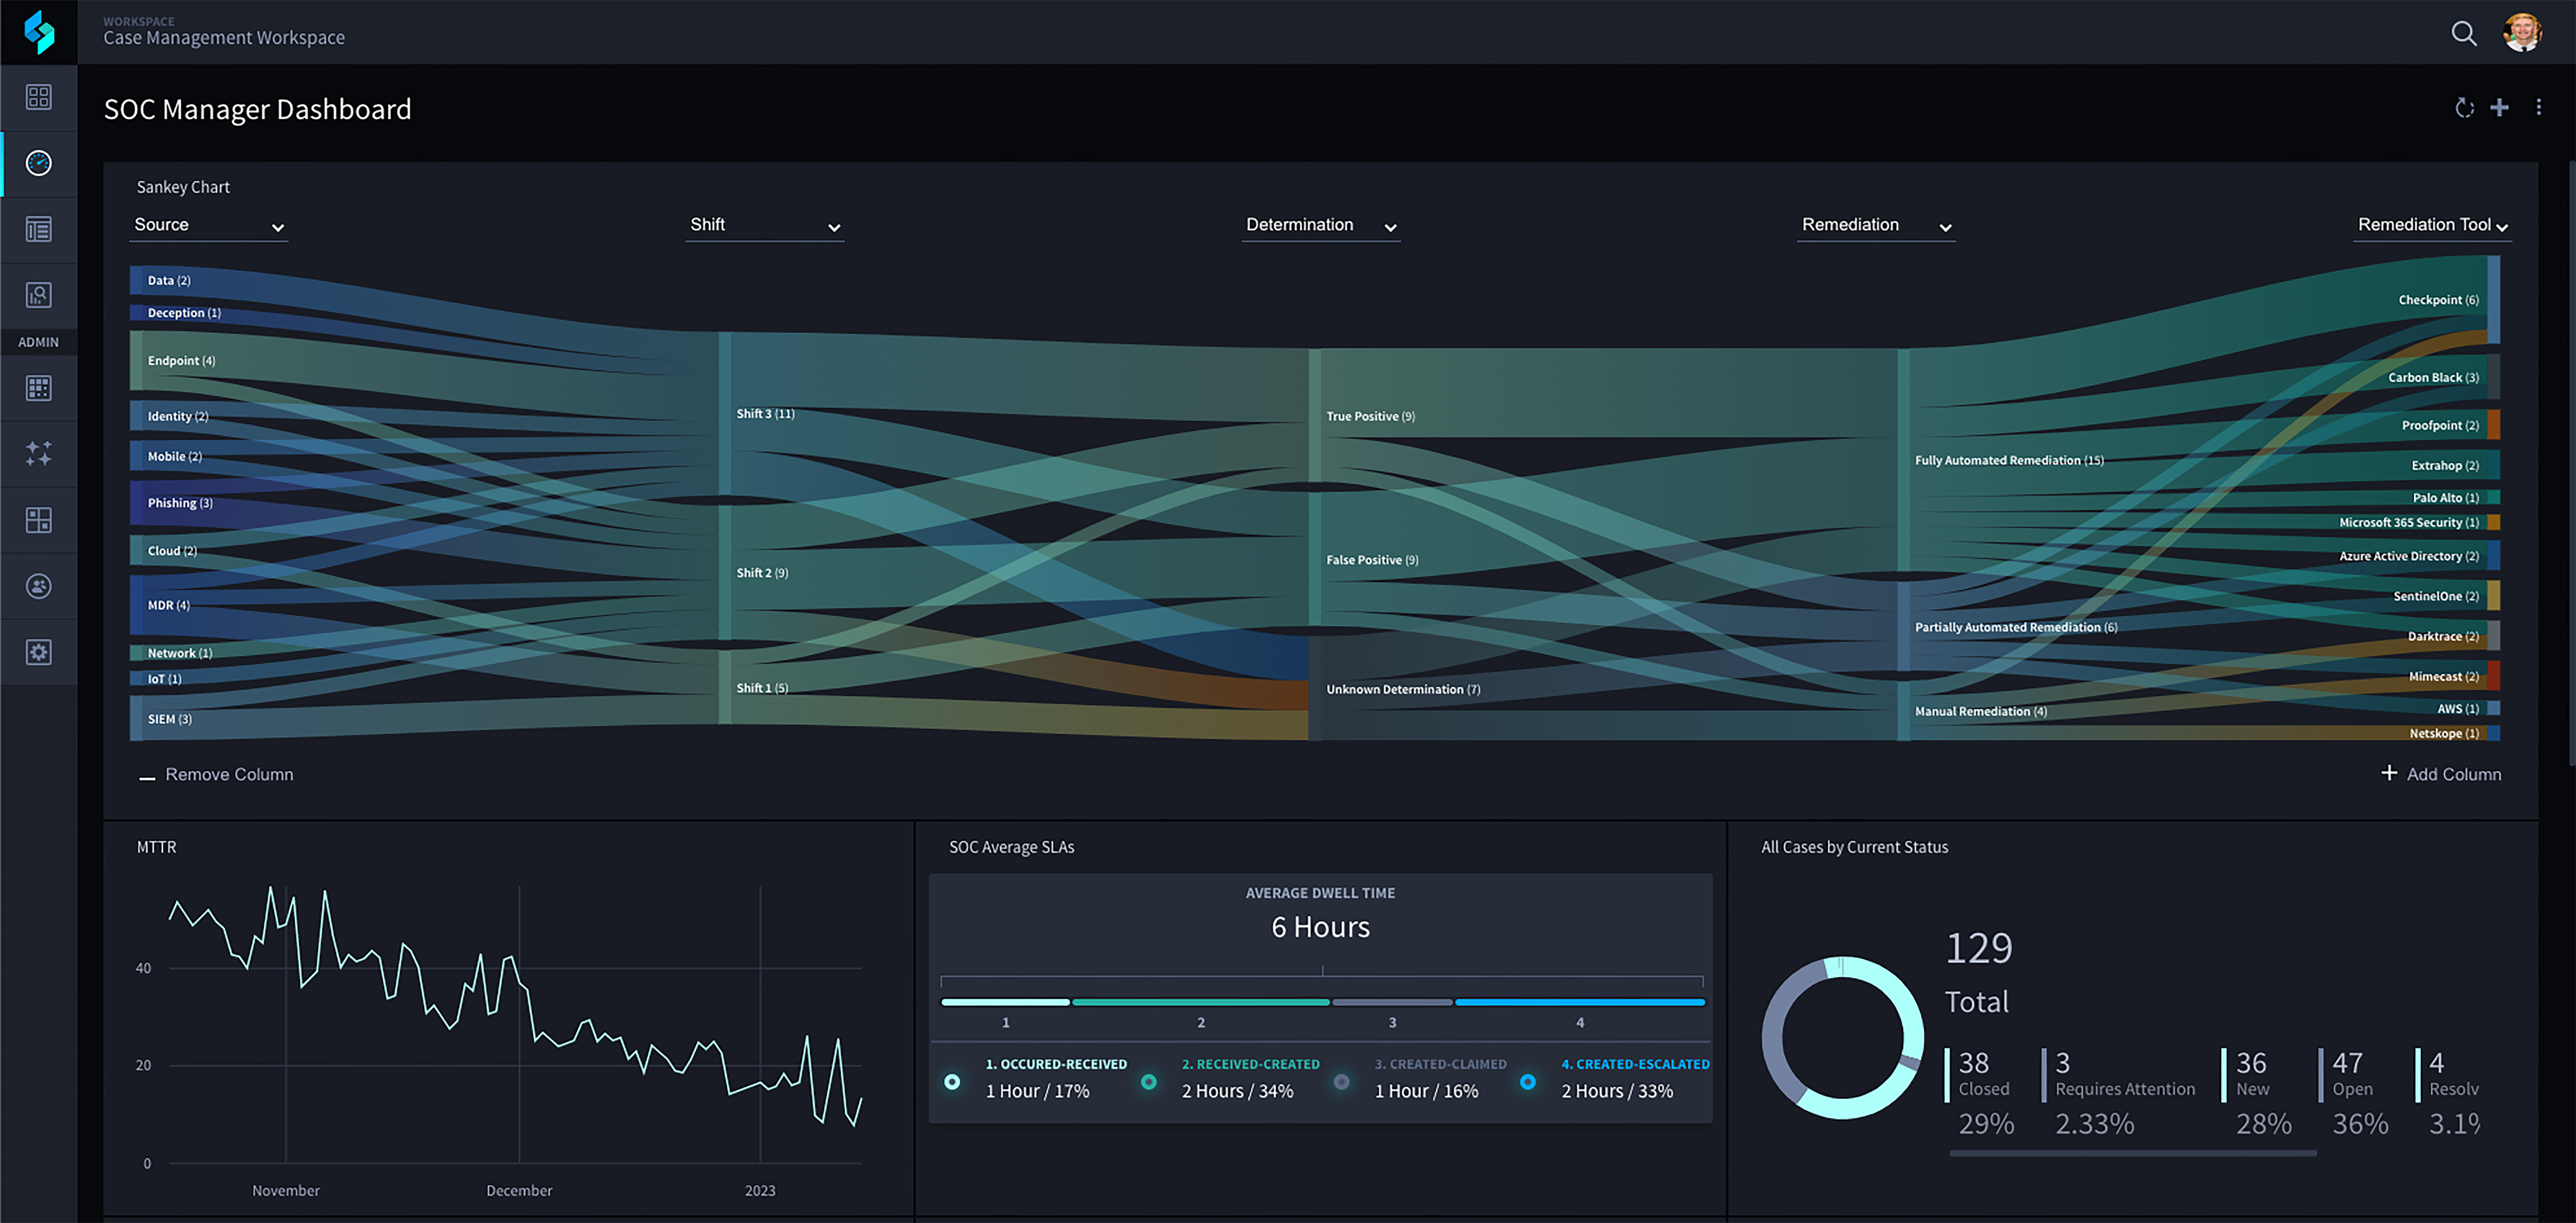
Turbine already does the hard part: continuous four-factor risk scoring, automated response for the 3-day tier, and an audit trail built in from the start. See exactly where your current stack falls short of the clock.
BOD 26-04 is a June 2026 Binding Operational Directive requiring U.S. federal civilian agencies to prioritize vulnerability remediation using a four-factor risk model: asset exposure, KEV status, exploit automatability, and technical impact, instead of flat, severity-based deadlines.y
It was issued June 10, 2026. Agencies must update policies immediately and reach full compliance with remediation timelines by December 7, 2026.
Yes. BOD 26-04 formally replaces both BOD 22-01 (2021, the KEV catalog directive) and BOD 19-02 (2019, internet-accessible systems).
Three days, for vulnerabilities that are publicly exposed, listed in the KEV catalog, exploitable via automation, and capable of granting total system control. This tier also requires forensic triage to check for prior compromise.
No. It’s binding only for Federal Civilian Executive Branch agencies, though FedRAMP-authorized cloud providers face related mandatory deadlines, and CISA encourages broader adoption. Given how quickly BOD 22-01’s KEV catalog became a commercial and insurance-industry standard, wide private-sector adoption of BOD 26-04’s model is expected.
FedRAMP-authorized cloud service providers must adopt new Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER) rulesets by December 7, 2026. Non-compliant providers have until March 7, 2027 under a corrective action plan before risking loss of FedRAMP authorization.
SSVC (Stakeholder-Specific Vulnerability Categorization) is CISA’s decision-tree methodology for evaluating vulnerability risk based on context rather than a single severity score. BOD 26-04’s four-factor model is built on SSVC principles, replacing CVSS-centric prioritization.

 English English
 Français
 Deutsch
 日本語
 한국어
 Português
 Español