

SWITCHING ISN’T THE REBUILD YOU’RE PICTURING
Your workflows come with you. Year one doesn’t cost you anything.
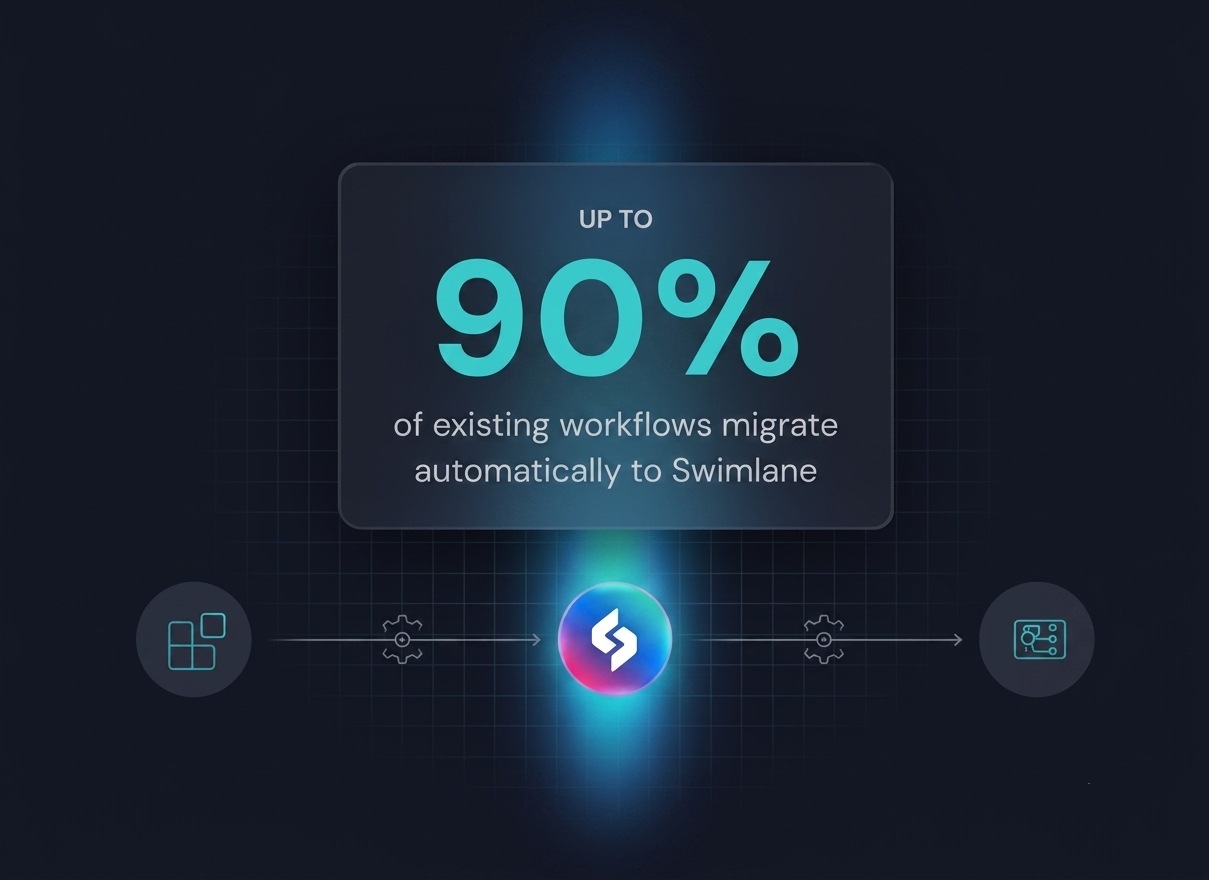
We migrate up to 90% of your existing XSOAR workflows automatically and handle the rest before go-live. You keep the automation your team built and leave the lock-in behind. Sign a 3-year agreement and up to your first year is on us.
| Splunk SOAR |  |
|||
|---|---|---|---|---|
| Scalability |  | Scaling complex workflows can require added tuning and support. |  | Executes 25M+ actions per day across high-volume SOC environments. |
| Playbook automation | | Advanced workflows may require deeper technical expertise. | | Low-code playbooks help teams build, update, and reuse workflows faster. |
| AI | | Limited native AI depth for investigation, reporting, and playbook support. | | Hero AI delivers fully agentic investigations, builder agents for playbooks, data visualization, and ingestion, all with LLM choice and the ability to build your own agents for use within playbooks. |
| AI governance | | Limited support for governed AI recommendations and approvals. | | Keeps AI-assisted actions controlled with analyst oversight and approval gates. |
| Integrations | | Offers third-party integrations across security and IT tools. | | Connects to any API, covering all SIEM, EDR, XDR, IAM, ITSM, cloud, email, threat intelligence, and vulnerability tools. |
| Case Management | | Supports case management within security workflows. | | Tracks evidence, ownership, escalation, risk, and response history in one customizable workspace. |
| Reporting and dashboards | | Reporting and dashboard flexibility may depend on configuration. | | Gives analysts, leaders, and compliance teams clear views into cases, workload, risk, and outcomes. |
| Deployment flexibility | | Works well for teams already invested in the Splunk ecosystem. | | Supports cloud, on-premises, hybrid, and complex enterprise environments. |
| Total cost of ownership | | Costs can grow through maintenance, customization, and scaling effort. | | Reduces overhead with agentic AI automation, reusable components, AI building agents, and flexible reporting. |
See Swimlane in Action
We migrate up to 90% of your workflows automatically and handle the rest. Up to a year free. Tell us where you’re starting from.
Reasons Why Customers Rely on Swimlane
- Leader in GenAI SOC Analyst platforms
- #1 rated security automation vendor on Gartner Peer Insights
- Turnkey solutions for automation beyond the Security Operations Center
Trusted By




Why Teams Look for a Splunk SOAR Alternative
SOC teams compare SOAR platforms when automation becomes difficult to scale, maintain, or measure. As security operations grow, they need faster playbook updates, stronger reporting, broader integrations, and AI-assisted workflows that keep analysts in control.

Simpler Playbook Management
Build, update, and reuse response workflows without relying on developers for every change.

Scalable AI SOC
Support high-volume triage, enrichment, escalation, and response across more use cases and teams.
Clearer Reporting and Dashboards
Track case status, response time, workload, risk, and automation impact in views built for analysts and leaders.
Broader Security Integrations
Connect critical security, IT, cloud, identity, and threat intelligence tools without adding new silos.

AI-Assisted Response
Use agentic AI to summarize cases, recommend next steps, support reporting, run autonomous investigations and keep approved actions governed.

It really takes time to understand all the sections from playbooks, integrations, automations etc where it lead to steeper learning curve.
Splunk SOAR Customer, Gartner Peer Insights

It felt like the product plateaued when Phantom was purchased by Splunk. From that point forward, changes were less frequent and support was less responsive.
Splunk SOAR Customer, Gartner Peer Insights
This will eat your budget if you dont know how your architecture will be.
Splunk SOAR Customer, Gartner Peer Insights
I do not like the fact that we cannot create alerts or customized reports with scripting inside.
Splunk SOAR Customer, Gartner Peer Insights
Switch to Swimlane with a Clear Path Forward
Moving from Splunk SOAR should not mean starting over. Swimlane Turbine helps teams review existing playbooks, reconnect key tools, rebuild workflows with agentic AI automation, and validate governance before scaling across the SOC.


Review Existing Workflows
Identify the playbooks worth keeping, the steps that need improvement, and the manual work ready for automation.
Reconnect Your Security Stack
Bring together the systems your SOC already relies on, including SIEM, EDR, XDR, IAM, ITSM, cloud, email security, vulnerability, threat intelligence, and ticketing tools.
Rebuild with Agnetic AI Automation
Use reusable components, flexible integrations, and an AI-generated playbook-building agent in our low-code automation studio to improve response workflows faster.
Validate Before You Scale
Confirm dashboards, case records, approvals, audit trails, escalation rules, and reporting before broader rollout.
Splunk SOAR vs Swimlane Frequently Asked Questions
What is the main difference between Splunk SOAR and Swimlane?
Splunk SOAR focuses on security orchestration and automated playbooks within the Splunk ecosystem. Swimlane Turbine extends security automation with agentic AI, low-code playbooks, case management, reporting, dashboards, integrations, and governed AI response in one flexible platform.
Is Swimlane a Splunk SOAR alternative?
Yes, Swimlane Turbine is a Splunk SOAR alternative for SOC teams that need scalable automation, AI-assisted investigation, flexible integrations, stronger reporting, and deployment options across cloud, on-premises, hybrid, and complex enterprise environments.
Can Swimlane replace Splunk SOAR playbooks?
Swimlane can help teams rebuild, refine, and scale existing SOAR workflows using a combination of AI agents and classic playbooks built using a low-code method through reusable components, flexible integrations, and AI-assisted automation support. This helps teams modernize response processes without starting from scratch.
Yes, Swimlane Turbine includes a playbook-generator AI agent and Turbine Canvas, a low-code building studio, that makes it easy to build playbooks and AI agents. With Canvas, analysts and engineers can create, update, and reuse response workflows faster without relying on developers for every change.
Yes. Swimlane connects with tools across the security stack, including SIEM, EDR, XDR, IAM, ITSM, cloud, email security, threat intelligence, vulnerability management, and ticketing systems.
 English
 Français
 Deutsch
 日本語
 한국어
 Português
 Español